
Recent observations have revealed that the threat actor JADEPUFFER has been engaging in destructive activities within a Microsoft Azure environment by exploiting compromised service principals.
Microsoft has identified this series of events as Storm-3168, characterizing it as an advancement in the threat actor’s tactics. The incident occurred in early June 2026 and lasted for approximately 18 hours.
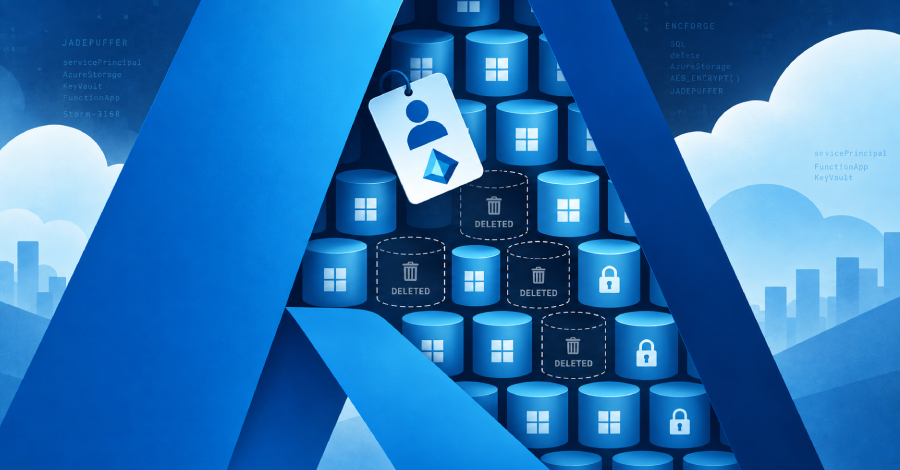
According to Yossi Weizman, Tushar Mudi, and the Microsoft Security Research team, the destructive actions involved the compromise of service principals and targeted various components within the Azure environment, including Storage Accounts, SQL databases, Key Vaults, Function Apps, Virtual Machines, and App Services.
JADEPUFFER, initially identified by Sysdig, utilized a large language model (LLM) to carry out a ransomware operation, exploiting a known security vulnerability in Langflow (CVE-2025-3248). The attack involved credential harvesting, encryption of Nacos service configuration files, database manipulation, and a ransom demand in Bitcoin.
Furthermore, the threat actor targeted the same Langflow instance with a second ransomware strain called ENCFORGE, specifically designed for artificial intelligence (AI) infrastructure. This strain searched for a wide range of file extensions related to AI models and macOS-specific files.
Sysdig highlighted that the AI model strung together various techniques to orchestrate a complete ransomware operation against internet-facing infrastructure. Microsoft’s analysis revealed that two compromised service principals were involved, with one focusing on reconnaissance while the other carried out destructive operations and credential collection.

The enumeration process targeted various Azure resources for an extended period, with over 300 read operations conducted. Subsequently, the second compromised service principal carried out discovery operations and engaged in destructive activities within a short timeframe.
During the attack, Azure Storage accounts were among the primary targets, with multiple deletion attempts made. Although some accounts were successfully deleted, others were protected by resource locks and deletion safeguards, demonstrating the importance of security measures even in the presence of compromised identities.
Microsoft noted that the compromise of the service principal was facilitated by previously exposed credentials in a public GitHub issue. Despite the removal of the exposed information, it remained accessible through edit history.
Additionally, Microsoft detected repeated probing from Storm-3168 against Azure App services, indicating automated or scripted attacks. The end goal of the attack appeared to be ransomware-related, aiming to disrupt the victim’s ability to recover from the damage.
As AI-orchestrated attacks become more prevalent, defenders are urged to leverage AI for enhanced detection and response capabilities. The evolving landscape of cyber threats underscores the need for proactive defense strategies in cloud environments.