Security
Ransomware Affiliate Betrayal: The WhatsApp RAT and Other Cyber Threats Unveiled

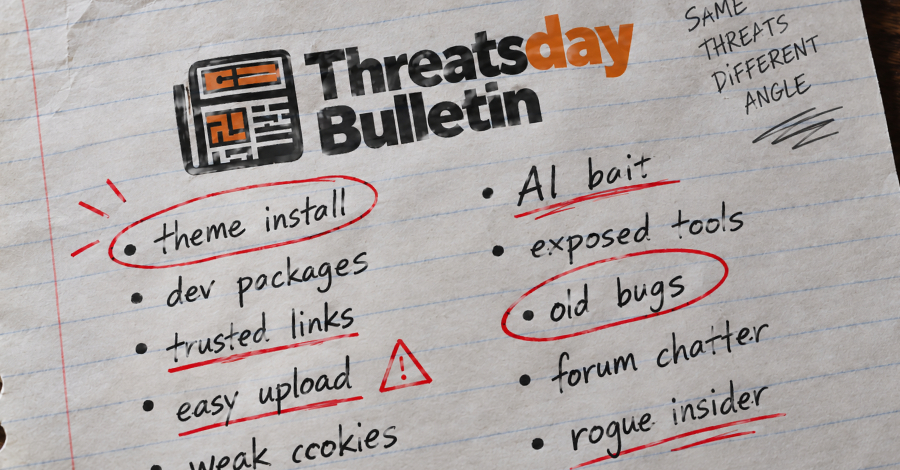
into valid JSON format. The attacker-operated staging service uncovered activities related to a breach at Mexican airline Viva Aerobus in late September 2026.
Recent Cybersecurity Incidents
Several cybersecurity incidents have come to light recently, shedding light on the vulnerabilities present in various systems. Let’s delve into the details of some of these incidents:
-
Exposed Infrastructure and Post-Exploitation Tools
A concerning discovery revealed that the exposed infrastructure contained a total of 17 named post-exploitation tools. These tools included credential-dumping scripts, Mimikatz output, SQL credential-testing utilities, and file-transfer tooling. The threat actor reportedly gained access to a Microsoft SQL server and utilized its xp_cmdshell functionality to run commands and deliver additional payloads. Interestingly, instead of setting up a separate outbound channel, the recovered tooling could read a file, split it into chunks, encode the content in Base64, and transmit those chunks through MSSQL query output. This activity raised a secondary exposure risk as unrelated internet hosts accessed the exposed infrastructure shortly after the initial victim-side activity, potentially compromising both the attacker’s tools and previously collected material.
-
Authentication Bypass in Yard Management System
Resecurity uncovered an authentication bypass vulnerability in an undisclosed yard management system (YMS). The vulnerability stemmed from two distinct weaknesses in the session-cookie mechanism of the application. Firstly, the session cookie was signed using a hardcoded secret identical to the cookie name, ‘session_secret_example.’ Secondly, the protected value of this signature was the user’s public database identifier (CUID) instead of a random session identifier. Exploiting these weaknesses could enable the generation of valid session cookies for any user whose IDs were accessible through the application’s API. This exploit could lead to session forgery for multiple employee accounts, including those with elevated privileges within the application.
-
Operation Blackout: Crackdown on Global Scam Centers
FBI Director Kash Patel shared details of Operation Blackout, a successful initiative that resulted in the seizure of $17 billion, hundreds of arrests, and the liberation of thousands of trafficked workers. This operation was part of law enforcement’s ongoing efforts to combat scam compounds that target vulnerable individuals, particularly the elderly, through fraudulent cryptocurrency investment schemes. Operation Blackout aims to identify, disrupt, and dismantle foreign scam compounds that prey on Americans. Patel emphasized the agency’s commitment to pursuing these criminal networks across regions, ensuring there is no safe haven for those targeting American citizens. The scam centers, described as purpose-built hubs, engage in coercive practices, confining workers and coercing them to contact targets through various means like social media, phone calls, and text messages.
One striking observation from these incidents is the apparent lack of caution exhibited by the attackers themselves. Some of them leave their tools exposed, while others engage in counterproductive activities like stealing from their own partners. It’s concerning to see that despite such careless behavior, these attackers can still exploit basic security flaws to achieve their malicious objectives. It’s a reminder that negligence in cybersecurity can have severe consequences.
Addressing the vulnerabilities highlighted in these incidents will require more than just a quick fix. It involves reevaluating old design choices, dealing with trusted software turning hostile, and preparing systems for future threats. Paying attention to seemingly mundane details is crucial as they often serve as entry points for potential security breaches. Stay vigilant and proactive in safeguarding your systems. That wraps up the latest updates in the cybersecurity landscape.







Conquering the Rubicon: A Review of the 2027 Jeep Wrangler 392

Trump administration accuses Microsoft of worker visa program abuse and restricts access

Ransomware Affiliate Betrayal: The WhatsApp RAT and Other Cyber Threats Unveiled

The Escapists: Breakout in 3D – A New Dimension of Freedom in 2027

Revolutionizing Energy Solutions for Data Centers and Military Vehicles: The Petra Power Initiative

Ultimate Travel Companion: Must-Have iPhone Apps for Stress-Free Journeys

Customized Koenigsegg CC850 Arrives in Denmark with Luxurious Gold Wheels

Revitalizing Windows: Microsoft’s Efforts to Breathe New Life into the Operating System

Unveiling the Dark Secrets of MonsterCloud’s Alleged Billing Scam: $19M in Ransoms Paid for Data Decryption

EU Takes Action Against Instagram and Facebook for Violating Illegal Content Rules

Warning: Facebook Creators Face Monetization Loss for Stealing and Reposting Videos

Facebook’s New Look: A Blend of Instagram’s Style

Facebook Compliance: ICE-tracking Page Removed After US Government Intervention

Facebook and Instagram to Reduce Personalized Ads for European Users

InstaDub: Meta’s AI Translation Tool for Instagram Videos

Reclaim Your Account: Facebook and Instagram Launch New Hub for Account Recovery

Meta discontinues Messenger apps for Windows and macOS

Breaking Updates: Meta Connect 2025 Unveils Latest Developments

Top 10 most INSANE Limited Edition Smartphones!

How Smart is the AI-Powered Huawei Mate 10 – with EMUI 8.0?

I used a 2012 Smartphone in 2018 – Here’s what happened.

How to send ANY file Anywhere!

NEW Oneplus 5T Sandstone White Unboxing – The Ultimate Oneplus 5T?

HUAWEI P20 – THE SMARTPHONE REVOLUTION IS HERE?

How OnePlus succeeded when they should have failed.

Samsung sent us THIS! #AD