Security
Urgent Alert: Critical PHP Vulnerability Threatens Website Security

PHP Security Patches Released to Fix Critical Vulnerabilities
PHP, a popular programming language for creating websites and web applications, has recently rolled out security patches to address two severe vulnerabilities. These vulnerabilities, rated at 9.2 out of 10 in severity, have the potential to cause significant damage if left unattended. Cybersecurity experts are advising website owners to apply the patches immediately or consider taking their systems offline temporarily.
The security patches were officially released at 10 AM ET today, urging PHP users to update their systems promptly. According to reports from cybersecurity firm watchTowr, the vulnerabilities are Remote Code Execution exploits affecting PHP versions from PHP 5 onwards. These exploits could allow attackers to execute malicious code on servers, potentially leading to website tampering and data theft.
The impact of these vulnerabilities is widespread, with an estimated 1.3 million internet-connected hosts at risk. WordPress sites, which account for over 40% of the internet, are also vulnerable as they run on PHP servers. Site owners are advised to manually apply the patches as automatic updates are not available for this fix.
Both the European Union Computer Emergency Response Team and the UK National Cyber Security Centre have issued warnings, suggesting companies isolate or take their internet-facing apps offline if immediate patching is not possible. Mobile OS developer GrapheneOS has already taken preemptive measures by temporarily shutting down their user forum due to emerging exploits. Gina Peter Banyard, a PHP developer, emphasizes that patching is crucial, and shutting down servers may be necessary in extreme cases.
Multiple cybersecurity organizations are advising PHP admins to prepare for potential mass attacks following the patch release. Cloudflare’s CTO, Dane Knecht, has reported early attacks targeting PHP sites and temporary firewall rule updates by Cloudflare to mitigate the risks.
Update, October 21st: The security patches have now been officially released.







Last Chance: Secure Your iPhone Duo This Friday with These Tips

6 Amazing SECRET Android Launchers (2017 / 2018)

Race Against Time: The Ultimate 2027 Production Test Drive

Xbox’s Return to the Office: Four-Day Work Week Mandate

End of an Era: Bioware’s Closure Marks the End of Mass Effect Development

Apple’s Strategic Plans for Surging Demand

The Evolution of Customer Discovery: Adapting to AI Search for Small Businesses

5 Common iPhone Slowdowns and How to Speed Them Up

Chery’s Luxeed: The Ultimate Luxury People Mover Arriving in Australia in 2027

EU Takes Action Against Instagram and Facebook for Violating Illegal Content Rules

Warning: Facebook Creators Face Monetization Loss for Stealing and Reposting Videos

Facebook’s New Look: A Blend of Instagram’s Style

Facebook Compliance: ICE-tracking Page Removed After US Government Intervention

Facebook and Instagram to Reduce Personalized Ads for European Users

InstaDub: Meta’s AI Translation Tool for Instagram Videos

Reclaim Your Account: Facebook and Instagram Launch New Hub for Account Recovery

Meta discontinues Messenger apps for Windows and macOS

Breaking Updates: Meta Connect 2025 Unveils Latest Developments
6 Amazing SECRET Android Launchers (2017 / 2018)

6 Value for Money Tech Products you NEED to try!

iPhone X Helicopter 1200ft Drop Test!! + Mous Case Review

7 UNBELIEVABLE Smartphone Magic Tricks!

Oneplus 5T vs Oneplus 1 – 3 Years Later.

Top 20 BEST Smartphones of 2017!

5 Amazing Upcoming Smartphone Features – 2018 / 2019

ULTIMATE Power Banks / The Best Power Banks (2017-2018)

TOP 5 BEST UPCOMING SMARTPHONES – 2018!!
-
 Facebook12 months ago
EU Takes Action Against Instagram and Facebook for Violating Illegal Content Rules
-
 Facebook1 year ago
Warning: Facebook Creators Face Monetization Loss for Stealing and Reposting Videos
-
 Facebook11 months ago
Facebook’s New Look: A Blend of Instagram’s Style
-
 Facebook1 year ago
Facebook Compliance: ICE-tracking Page Removed After US Government Intervention
-
 Facebook11 months ago
Facebook and Instagram to Reduce Personalized Ads for European Users
-
 Facebook1 year ago
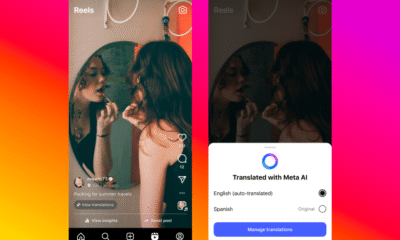
InstaDub: Meta’s AI Translation Tool for Instagram Videos
-
 Facebook11 months ago
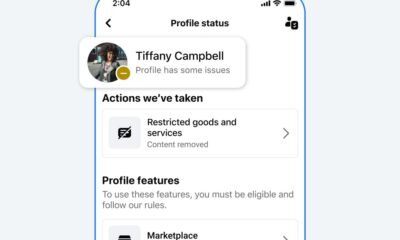
Reclaim Your Account: Facebook and Instagram Launch New Hub for Account Recovery
-
 Apple1 year ago
Meta discontinues Messenger apps for Windows and macOS