

CISA Warns of Ransomware Attacks Exploiting BeyondTrust RCE Flaw A critical vulnerability, CVE-2026-1731, in BeyondTrust’s Remote Support product is being actively exploited by hackers, as highlighted...

Employee accounts are increasingly targeted in cyber-attacks, with one in three incidents involving compromised credentials. To better assess cyber risk, insurers and regulators now focus on...


Japanese tech giant Advantest hit by ransomware attack Advantest Corporation has revealed that it fell victim to a ransomware attack targeting its corporate network, potentially compromising...


Authored by Ivan Milenkovic, Vice President Risk Technology EMEA, Qualys Over the past decade, there has been a prevailing belief that if developers could take on...

The Case of Oleksandr Didenko: Ukrainian National Sentenced for Providing Stolen Identities to North Korean IT Workers A Ukrainian individual, Oleksandr Didenko, has been handed a...

The ever-evolving cyber threat landscape is constantly changing, with new risks, tactics, and security gaps emerging across various platforms, tools, and industries simultaneously. This week, significant...
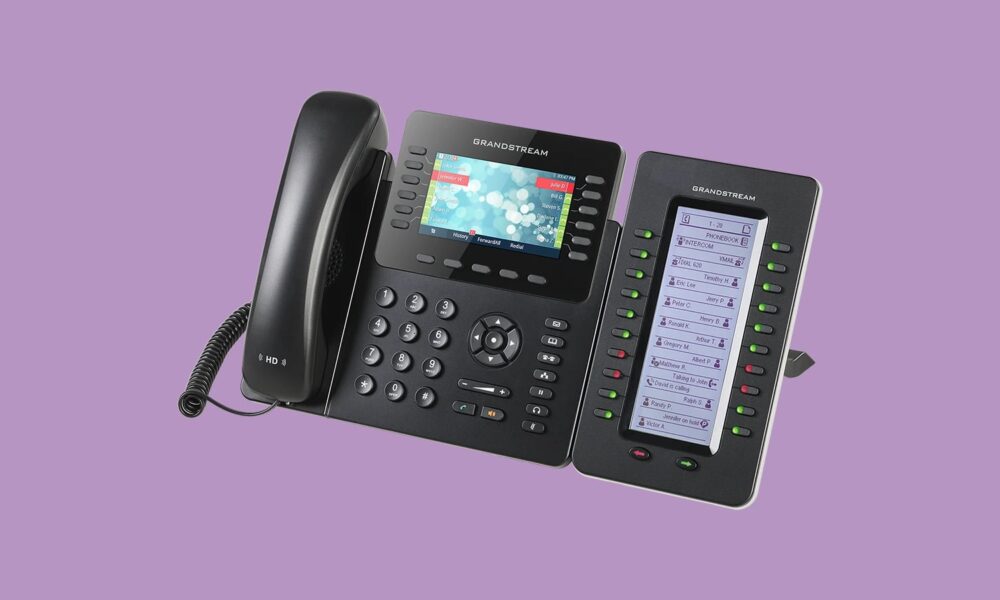

Grandstream VoIP Vulnerability Exposed: Root Privileges Compromised In a recent discovery, a critical vulnerability in the Grandstream GXP1600 series VoIP phones has been unearthed. This flaw...

A Hacker’s Mischievous Exploits with an AI Coding Tool In a recent incident, a hacker managed to deceive a popular AI coding tool into installing OpenClaw,...


Texas Attorney General Takes Legal Action Against TP-Link Over Alleged China Ties A recent lawsuit filed by Texas Attorney General Ken Paxton accuses router-maker TP-Link of...


The Urgency of Patching Vulnerabilities: CISA’s Directive to Government Agencies Recent reports from the U.S. Cybersecurity and Infrastructure Security Agency (CISA) have highlighted the critical need...


Subscribe to our weekly newsletter below and never miss the latest News or an exclusive offer.