Cars
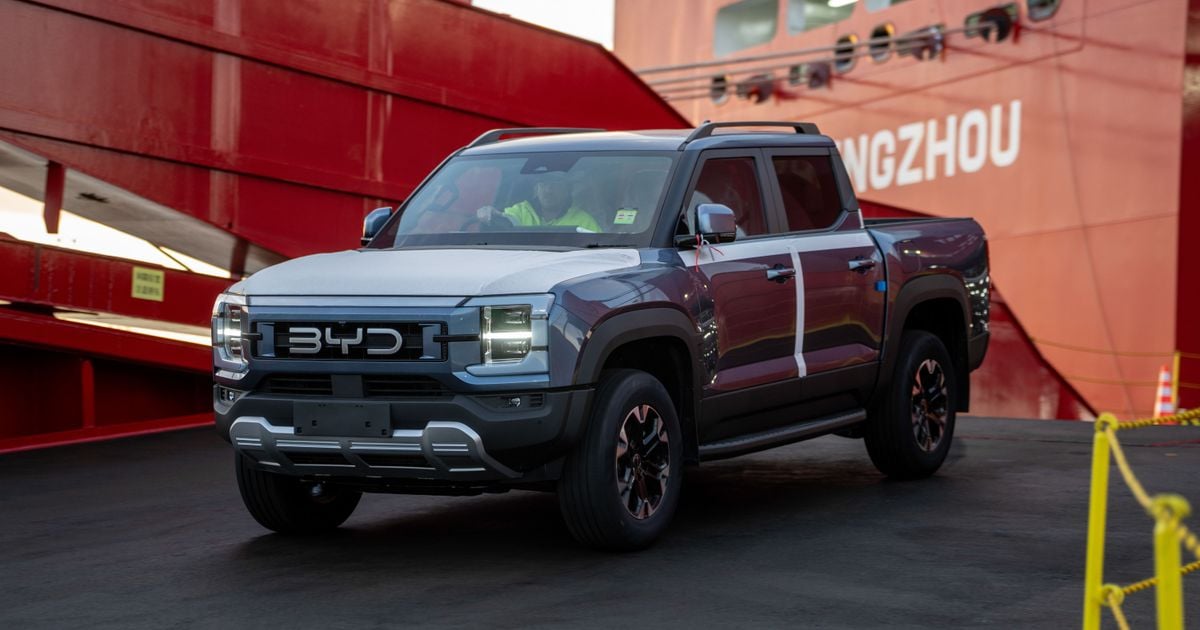
BYD’s Shark 6 Software Vulnerability Uncovered in Hacking Investigation

Fortify Labs Highlights Car Manufacturer Access Concerns
Fortify Labs recently released a statement regarding the Four Corners episode, emphasizing their aim to showcase the potential risks associated with remote access to connected vehicles. The organization clarified that their goal was to demonstrate how such access could be exploited rather than gaining initial entry into the vehicle.
The statement further emphasized that manufacturers have the capability to remotely access vehicles, execute commands, and provide over-the-air (OTA) updates. While acknowledging BYD’s strong security measures in certain areas of the vehicle, Fortify Labs hopes to prompt industry-wide improvements by highlighting vulnerabilities and supporting the implementation of draft ADRs.
Additionally, Fortify Labs advocated for a cybersecurity rating system for connected cars, enabling consumers to assess the security of data storage and collection. The organization stressed the importance of not blindly trusting vehicle manufacturers and noted that security concerns extend beyond Chinese manufacturers to include vehicles from other regions like the United States, Europe, and Asia.
Concerns were raised about the global nature of these risks, emphasizing that countries worldwide should be vigilant. Fortify Labs underscored the need for greater transparency and accountability in the automotive industry to address cybersecurity challenges effectively.
MORE: ‘Urgent’ calls for greater transparency on data collection following report on Chinese car hacking







Samsung Galaxy S9+ Unboxing! (Clone)

BYD’s Shark 6 Software Vulnerability Uncovered in Hacking Investigation

24/7 Surveillance: The Controversial Reality of Amazon’s Delivery Driver Smart Glasses

October 2026’s PS Plus Lineup: Join the Battle in EDF: World Brother 2

Unleashing the Power of the Galaxy Tab S12 Ultra: A 24-Hour Journey with Multiple Expletives

Startup Safety: The Ultimate Guide to Protecting Your Business as a First-Time Founder

Insights from AI Experts: Evaluating Trump’s latest safety initiative

California Highway Patrol Unveils Last Chevrolet Camaro in Fleet

Revolutionizing Home Entertainment: The Fire TV Stick 4K’s Power-Saving Feature

EU Takes Action Against Instagram and Facebook for Violating Illegal Content Rules

Warning: Facebook Creators Face Monetization Loss for Stealing and Reposting Videos

Facebook’s New Look: A Blend of Instagram’s Style

Facebook Compliance: ICE-tracking Page Removed After US Government Intervention

Facebook and Instagram to Reduce Personalized Ads for European Users

InstaDub: Meta’s AI Translation Tool for Instagram Videos

Reclaim Your Account: Facebook and Instagram Launch New Hub for Account Recovery

Meta discontinues Messenger apps for Windows and macOS

Breaking Updates: Meta Connect 2025 Unveils Latest Developments
Samsung Galaxy S9+ Unboxing! (Clone)

Unboxing the First Ever Samsung Galaxy S!!

Huawei P Smart – Huawei’s new Killer Budget Smartphone!

MYSTERY Package from Xiaomi – HUGE UNBOXING!

5 ways you’re using your Smartphone wrong.

THE INSANE DUAL BATTERY SMARTPHONE!

ELEPHONE U PRO UNBOXING AND REVIEW!

Mrwhosetheboss – 1 Million Subscribers

The Surprising TRUTH about Samsung – 15 things you did not know.
-
 Facebook11 months ago
EU Takes Action Against Instagram and Facebook for Violating Illegal Content Rules
-
 Facebook12 months ago
Warning: Facebook Creators Face Monetization Loss for Stealing and Reposting Videos
-
 Facebook10 months ago
Facebook’s New Look: A Blend of Instagram’s Style
-
 Facebook12 months ago
Facebook Compliance: ICE-tracking Page Removed After US Government Intervention
-
 Facebook10 months ago
Facebook and Instagram to Reduce Personalized Ads for European Users
-
 Facebook12 months ago
InstaDub: Meta’s AI Translation Tool for Instagram Videos
-
 Facebook10 months ago
Reclaim Your Account: Facebook and Instagram Launch New Hub for Account Recovery
-
 Apple12 months ago
Meta discontinues Messenger apps for Windows and macOS