

Chinese Cyberspies Breach Singapore’s Largest Telcos Last year, a Chinese threat actor known as UNC3886 infiltrated Singapore’s four major telecommunication service providers – Singtel, StarHub, M1,...


SmarterTools Network Breached by Hackers Utilizing Flaw in Own Software Last week, SmarterTools confirmed that the Warlock ransomware gang successfully breached their network by exploiting a...


Russian Hackers Exploit Recently Patched Microsoft Office Bug Reports from Ukraine’s Computer Emergency Response Team (CERT) reveal that Russian hackers are taking advantage of CVE-2026-21509, a...


Initial Access Broker TA584 Expands Operations with Tsundere Bot for Ransomware Attacks An active initial access broker known as TA584 has recently been utilizing the Tsundere...


Mustang Panda, a Chinese cyber espionage group, has recently upgraded its CoolClient backdoor to a new version capable of extracting login information from web browsers and...


Cyberattack on Poland’s Power Grid Linked to Russian Hacking Group Sandworm In a recent cyberattack on Poland’s power grid in late December 2025, the Russian state-sponsored...


The Rise of StealC Malware: Unveiling the Vulnerabilities Security researchers recently uncovered a critical cross-site scripting (XSS) flaw in the web-based control panel utilized by operators...


Chinese-Speaking Threat Actors Suspected in Targeting VMware ESXi with Compromised SonicWall VPN Appliance Recent cybersecurity findings suggest that threat actors fluent in Chinese may have utilized...


Update: The article has been revised to accurately reflect that the ShinyHunters deny involvement in the incident. The story and title have been adjusted accordingly. Threat...


A recent instance of the ToneShell backdoor, commonly associated with Chinese cyberespionage operations, has been distributed through a kernel-mode loader in targeted attacks against governmental entities....

Discover the Exciting World of Keep Driving RPG Embark on a journey with Brendy, Nic, Julian, and many others in...

Grand Theft Auto VI: The Album Set to Launch Alongside the Game Rockstar Games has recently revealed that Grand Theft...

The Immersive World of Tokyo Walled City: A Cyberpunk Adventure on the Horizon Embark on a journey through the neon-lit...

Japan Unveiled as Third Map in Crazy Taxi: World Tour Sega has recently announced that Japan will be the latest...

Heart Machine Faces Layoffs Amid Funding Withdrawal Heart Machine, the renowned US-based game development studio behind titles such as Hyper...

Twitch CEO Confirms Exciting Future for Streamers with GTA 6 Online Amidst the speculation surrounding the highly anticipated GTA 6...

Zero Parades: For Dead Spies – A Pleasant Surprise Upon the release of ZA/UM’s Zero Parades: For Dead Spies, there...

Capcom Announces Removal of Character Edit Microtransactions in Monster Hunter Wilds: Ascendance By [Author Name] In a move that has...

The era of AI translation in 2026 brings about a unique challenge that many businesses may not be fully aware...

Angle Health Raises $200 Million Series C with $400 Million Tender Offer In the rapidly evolving startup landscape, Angle Health,...

Penelope Health Secures €87 Million Funding and Partners with Thoreau for Real-time Payments and Clinical Rules Penelope Health, a cutting-edge...

The Benefits of Prototyping in Product Development Prototyping is a crucial step in product development that allows ideas to be...

The Rise of PrismML: Revolutionizing AI with Groundbreaking Compression Technology PrismML, the AI lab that is quickly making a name...
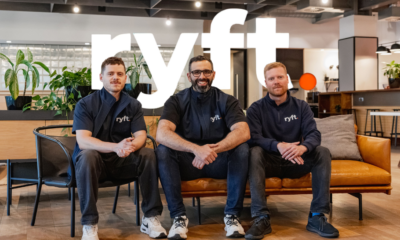

Manchester-based payments company Ryft has recently secured a €23 million (£20 million) Series B funding round as part of efforts...

Startups have always been attractive targets for scammers. They move quickly, rely heavily on digital tools and often have fewer...
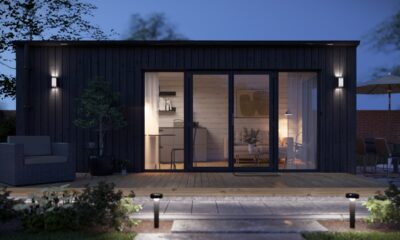

Exploring the Rise of Garden Rooms in Ireland The home improvement landscape in Ireland is undergoing a transformation, with a...
Subscribe to our weekly newsletter below and never miss the latest News or an exclusive offer.